Top Stories
Recent Posts
-
Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
Dell has released security updates to address multiple critical security flaws in…
-
GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers
A critical flaw in GitLab’s AI Gateway could let a logged-in user…
-
Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
Government and policy organizations across Asia have become the target of a…
-
OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
OpenAI has parted ways with three members of its safety team after…
-
Why CISOs Struggle to Answer the Board’s Three Hardest Questions, and How to Fix the Report
The quarterly board meeting is two weeks out. The security team is…
-
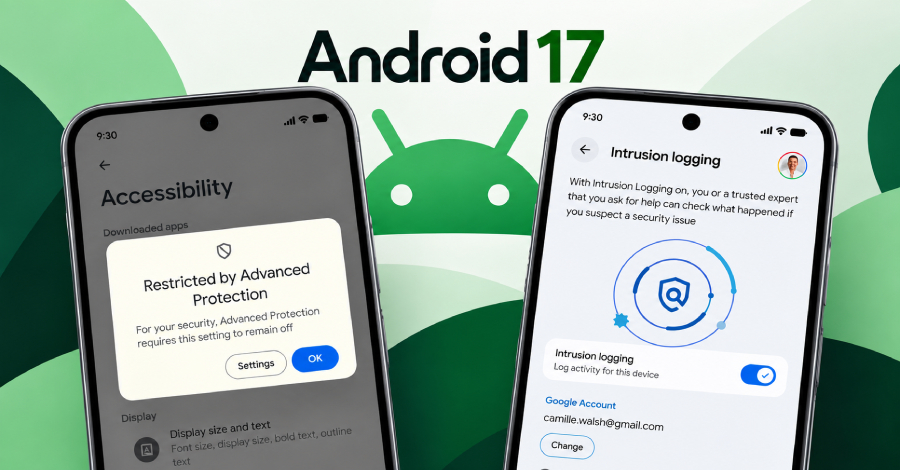
Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
Google has announced a new security measure that limits access to Android’s…
-
WordPress Backdoor Rebuilds Itself After Cleanup Using Files, Database, and Shared Memory
Cybersecurity researchers have shed light on a WordPress compromise in which threat…
-
Bitget Confirms Third-Party Zero-Day Behind $387.5 Million Cryptocurrency Theft
Cryptocurrency exchange Bitget on Wednesday confirmed that attackers who stole $387.5 million…
-
MetaMask Security Incident Prompts Exit of Affected Ethereum Validators
MetaMask on Thursday said it’s responding to what it described as an…
-
Citrix NetScaler Post-Exploitation Payload Creates Superuser, Maps Web Shell to CSS-Like URLs
Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability…
