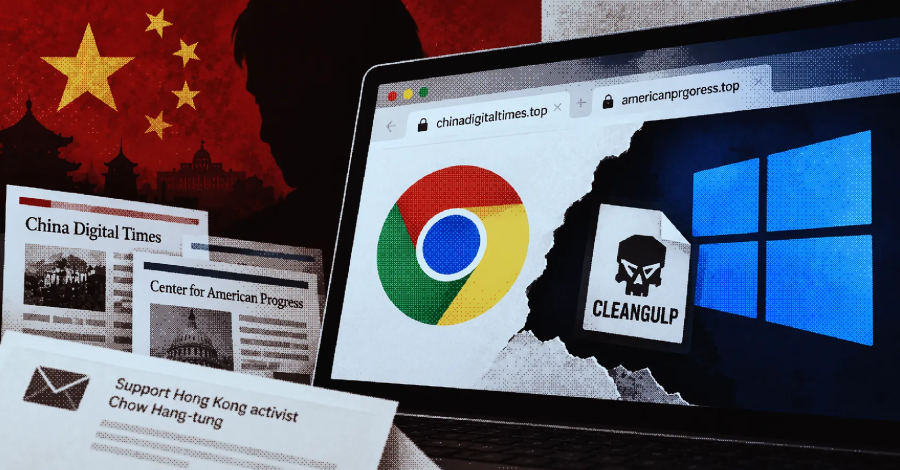

A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites.
The attacks, detected on September 3 and 4, 2026, involved the chaining of two vulnerabilities in Chrome (CVE-2026-85046, CVE-2026-87491) and one impacting Windows Advanced Local Procedure Call (CVE-2026-85880) to break out of the browser’s sandbox and achieve remote code execution.
“UTA0565 masqueraded as various entities including media organizations and a non-governmental organization (NGO),” Volexity researchers Damien Cash and Tom Lancaster said in an analysis published this week. “Notably, this threat actor’s campaigns differed from previously documented attacks by using multiple fake websites to deceive victims.”
One such campaign targeted Asian government entities with Chinese- and English-language phishing emails that urged recipients to support Hong Kong activist Chow Hang-tung and masqueraded as the Center for American Progress (CAP). Chow was sentenced to seven years and three months in prison earlier this month.
Leave a Reply