News
-
Google Play Early Access Abused to Push Thousands of Deceptive Android Apps
Bad actors are misusing Google Play’s Early Access program to push deceptive…
-
Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs…
-
Webinar: Learn How to Answer “Are We Exposed?” Faster After a New CVE
A major vulnerability is disclosed. The alert lands immediately. Then comes the…
-
DeepSeek Harness Flaw Let AI Agents Disable Their Own File Sandbox Without Approval
A flaw in DeepSeek Harness, DeepSeek’s open-source tool for running AI coding…
-
Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox
Google on Thursday released updates to patch 230 security vulnerabilities, including one…
-
N-able N-central Pre-Auth RCE Flaw Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a…
-
Slim Spider Steals Crypto Custody Secrets From Brazilian Financial Institution
A previously undocumented financially motivated threat actor has been linked to attacks…
-
FreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials
A flaw in FreeIPA lets a client that has never logged in…
-
Adobe Patches Magento Zero-Day Exploited to Deploy Rust Backdoor and PHP Web Shell
Adobe on Monday released security patches to address a maximum-severity flaw impacting…
-
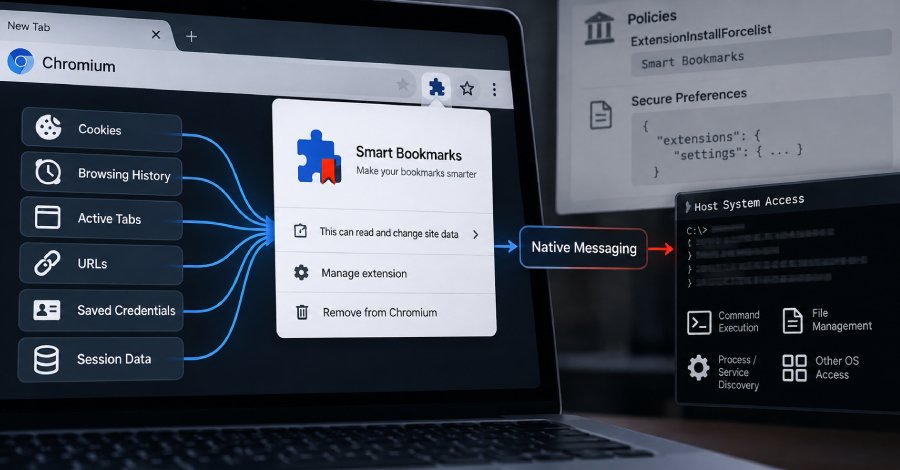
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called…
