News
-
CISA Orders Removal of Unsupported Edge Devices to Reduce Federal Network Risk
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered Federal Civilian…
-
Asian State-Backed Group TGR-STA-1030 Breaches 70 Government, Infrastructure Entities
A previously undocumented cyber espionage group operating from Asia broke into the…
-
How Samsung Knox Helps Stop Your Network Security Breach
As you know, enterprise network security has undergone significant evolution over the…
-
Compromised dYdX npm and PyPI Packages Deliver Wallet Stealers and RAT Malware
Cybersecurity researchers have discovered a new supply chain attack in which legitimate…
-
The Buyer’s Guide to AI Usage Control
Today’s “AI everywhere” reality is woven into everyday workflows across the enterprise,…
-
Critical n8n Flaw CVE-2026-25049 Enables System Command Execution via Malicious Workflows
A new, critical security vulnerability has been disclosed in the n8n workflow…
-
China-Linked Amaranth-Dragon Exploits WinRAR Flaw in Espionage Campaigns
Threat actors affiliated with China have been attributed to a fresh set…
-
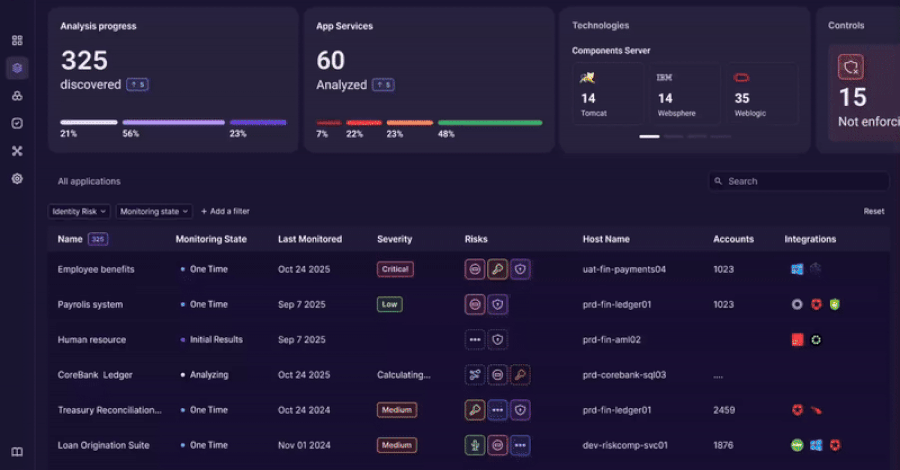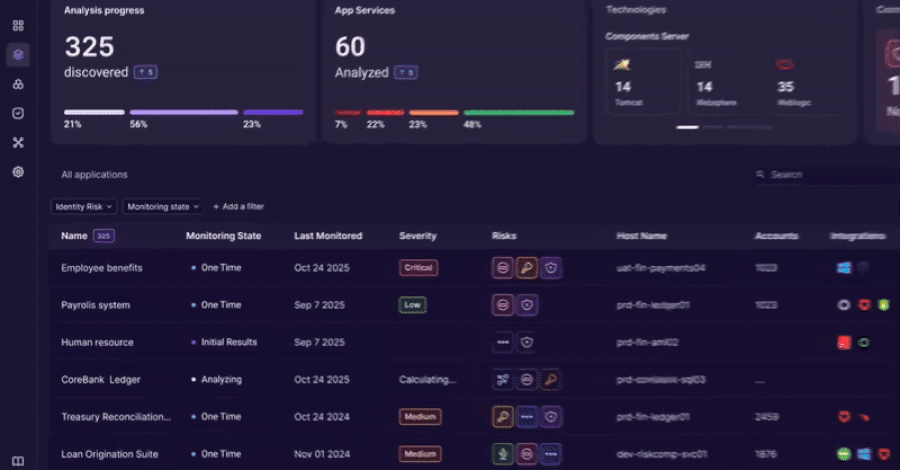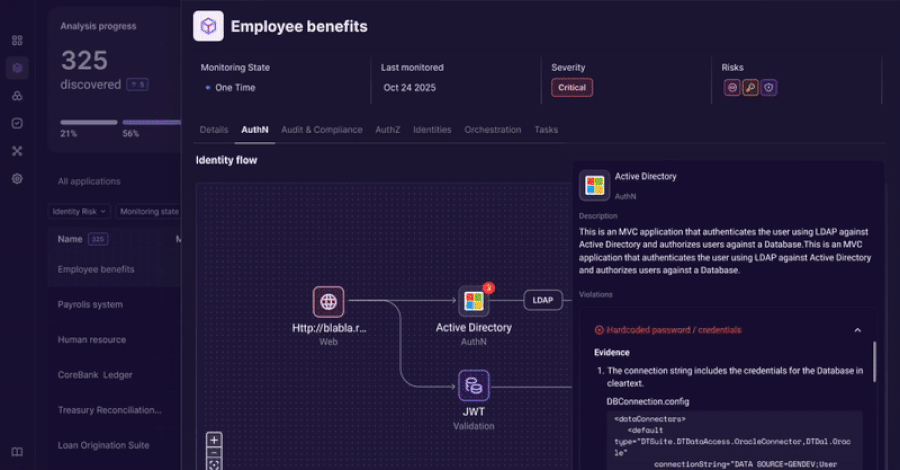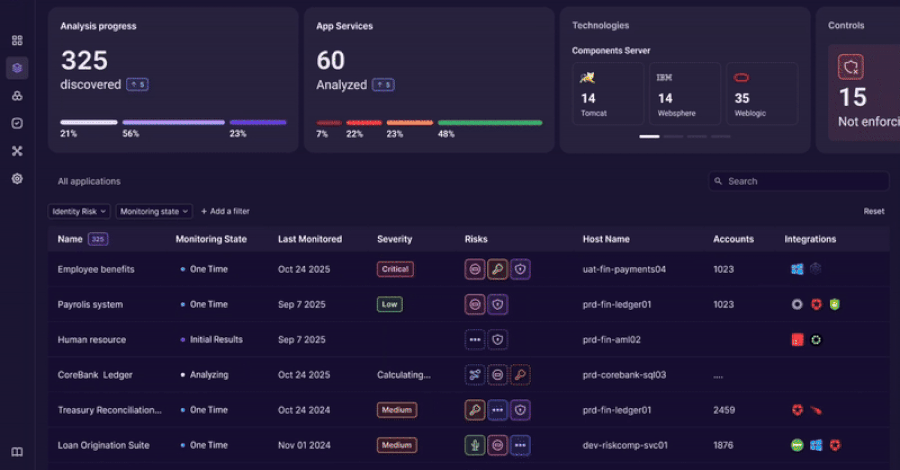
Orchid Security Introduces Continuous Identity Observability for Enterprise Applications
An innovative approach to discovering, analyzing, and governing identity usage beyond traditional…
-
[Webinar] The Smarter SOC Blueprint: Learn What to Build, Buy, and Automate
Most security teams today are buried under tools. Too many dashboards. Too…
-
Hackers Exploit Metro4Shell RCE Flaw in React Native CLI npm Package
Threat actors have been observed exploiting a critical security flaw impacting the…
