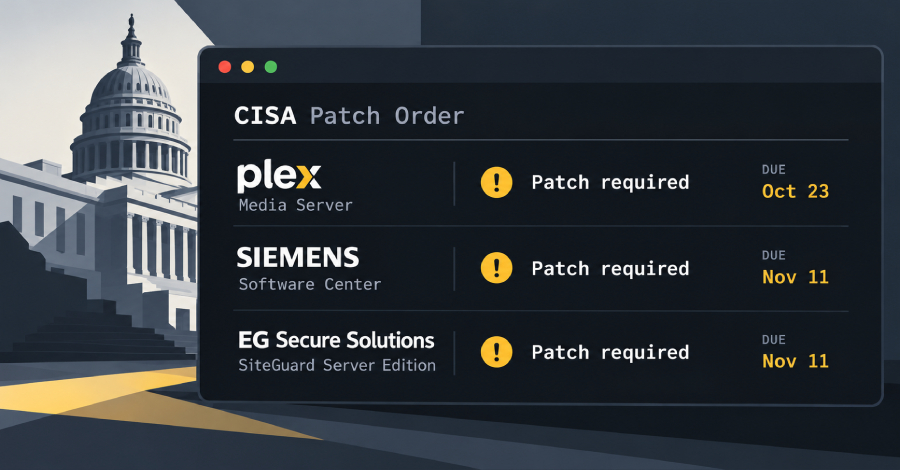

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including four vulnerabilities impacting Plex Media Server that’s collectively called Plex2Shell.
The vulnerabilities are listed below –
- CVE-2026-96652 (CVSS score: 5.3) – Plex Media Server Server-Side Request Forgery (SSRF) vulnerability
- CVE-2026-96654 (CVSS score: 6.9) – Plex Media Server improper neutralization of encoded URI schemes in a web page Vulnerability
- CVE-2026-96655 (CVSS score: 5.3) – Plex Media Server Server-Side Request Forgery (SSRF) vulnerability
- CVE-2026-96656 (CVSS score: 8.6) – Plex Media Server external control of file name or path Vulnerability
According to security researcher Zach Main, who discovered and reported the vulnerabilities, a remote attacker could chain the four vulnerabilities to achieve unauthenticated remote code execution. The issues were addressed in Plex Media Server 1.43.3.10861 released on August 3, 2026.
Leave a Reply