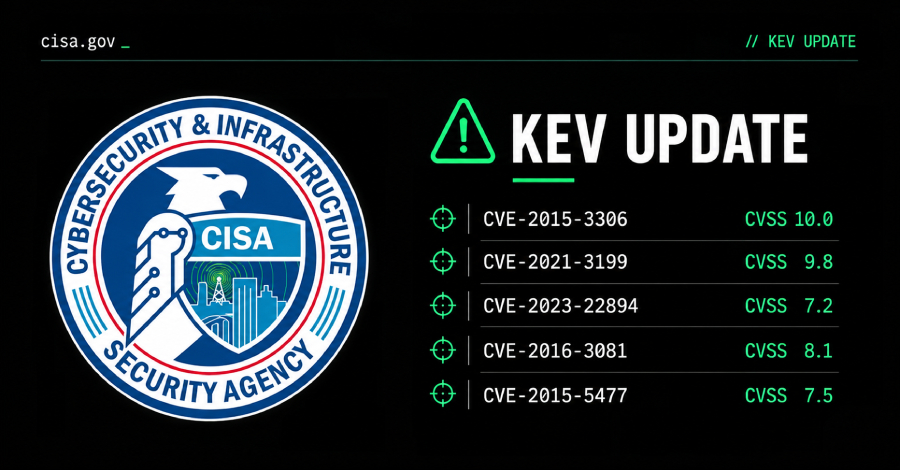

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon.
The vulnerabilities in question are listed below –
- CVE-2015-3306 (CVSS score: 10.0) – An improper access control vulnerability in ProFTPD that could allow remote attackers to read and write to arbitrary files via the site cpfr and site cpto commands.
- CVE-2021-3199 (CVSS score: 9.8) – A path traversal vulnerability in ONLYOFFICE Docs that can occur when JSON Web Token (JWT) is used, via a “/..” sequence in an image upload parameter and could allow for remote code execution.
- CVE-2023-22894 (CVSS score: 7.2) – A cleartext storage of sensitive information vulnerability in Strapi that could allow an attacker with access to the admin panel to discover sensitive user details via the query filter.
- CVE-2016-3081 (CVSS score: 8.1) – A command injection vulnerability in Apache Struts that could allow a remote attacker to execute arbitrary code via method:prefix when Dynamic Method Invocation is enabled.
- CVE-2015-5477 (CVSS score: 7.5) – A reachable assertion vulnerability in ISC BIND that could allow a remote attacker to cause a denial-of-service via TKEY queries.
The addition of the five vulnerabilities coincides with a joint advisory released by Australia, Canada, Japan, New Zealand, Spain, the U.K., and the U.S. warning of attacks enabled by a China-based cybersecurity company known as Integrity Technology Group.
Leave a Reply